

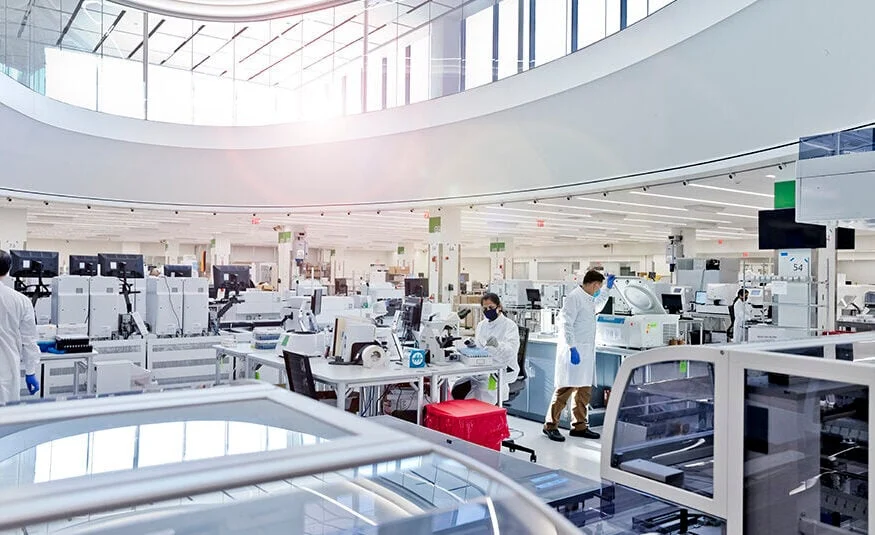
Secaucus, NJ – October 26, 2023 – Quest Diagnostics, a titan in the medical laboratory services industry, has confirmed a significant cybersecurity incident that led to the immediate shutdown of access to its Quanum Lab Services Manager platform. The company disclosed the breach in a regulatory filing on October 22, revealing that unauthorized access was detected the previous day. This event has raised serious concerns about the potential exposure of sensitive patient records, marking another unsettling chapter in the ongoing cybersecurity challenges facing the healthcare sector.
The Quanum platform is a critical digital tool for Quest Diagnostics, enabling specific clients, including healthcare providers, to efficiently order laboratory tests and retrieve patient results. The swift action to suspend access underscores the gravity with which Quest Diagnostics is treating this intrusion, as the company now works in collaboration with federal law enforcement and external cybersecurity experts to investigate the full scope of the breach.
While Quest Diagnostics has acknowledged that "certain patient records may have been accessed," the precise number of individuals affected and the specific nature of the compromised information remain undisclosed. This lack of immediate detail has amplified anxieties among patients and healthcare professionals alike, highlighting the persistent vulnerability of digital health infrastructure to malicious actors.
Chronology of the Incident: A Rapid Response to a Digital Threat
The timeline of events, as detailed by Quest Diagnostics, illustrates a swift reaction to the detected unauthorized access.
October 21, 2023: Quest Diagnostics personnel detected unauthorized access to their Quanum Lab Services Manager platform. This discovery triggered an immediate internal investigation and the initiation of security protocols.
October 22, 2023: Quest Diagnostics formally disclosed the cybersecurity breach in a filing with the U.S. Securities and Exchange Commission (SEC). On the same day, the company also notified federal law enforcement agencies about the incident.
October 23, 2023: In an effort to provide transparency and address public inquiries, Quest Diagnostics launched a dedicated Frequently Asked Questions (FAQ) page on its corporate website. This page was intended to offer initial information and guidance to affected parties.
Ongoing: The incident is currently under comprehensive investigation by Quest Diagnostics, with the support of specialized external cybersecurity firms. The company has maintained that its core business operations remain unaffected and continue to function normally, a crucial point for the millions of patients and healthcare providers who rely on their services daily.
The company’s decision to "pause access to the system" upon learning of the cyberattack was a decisive measure aimed at containing the breach and preventing further unauthorized data exfiltration. This decisive action, while disruptive, is a standard cybersecurity practice to isolate a compromised system and allow for a thorough forensic analysis.
Supporting Data: The Extensive Reach of Quest Diagnostics
To comprehend the potential impact of this breach, it is essential to understand the sheer scale of Quest Diagnostics’ operations and its pervasive role in the American healthcare landscape. As one of the nation’s largest providers of diagnostic testing, Quest Diagnostics serves a vast network of clients and individuals.
- Client Base: The company provides essential diagnostic testing and related services to a broad spectrum of healthcare entities, including individual physicians, hospitals, health plans, and directly to patients.
- Accessibility: Quest Diagnostics boasts an extensive network of over 7,770 patient access points across North America, ensuring that its testing services are readily available to a significant portion of the population.
- Market Penetration: The company’s comprehensive test offerings, ranging from routine blood work to highly specialized screenings for complex diseases like cancer, are accessible to more than 90% of U.S. insured lives.
- Annual Reach: Annually, Quest Diagnostics serves approximately one-third of all American adults, a staggering figure that underscores its integral role in public health.
- Provider Partnerships: The company is a critical partner for the healthcare ecosystem, handling testing for an estimated half of all physicians and hospitals in the United States each year.
- Workforce and Expertise: Quest Diagnostics employs a substantial workforce of over 57,000 individuals, including a robust medical and scientific staff comprising more than 700 physicians, demonstrating the depth of expertise within the organization.
This extensive reach means that any compromise of patient data could have far-reaching consequences, impacting a substantial segment of the U.S. population. The Quanum platform, as a direct interface for ordering and receiving test results, is a particularly sensitive area for data access.

Official Responses: A Commitment to Transparency and Investigation
Quest Diagnostics has issued statements and established dedicated resources to communicate with the public and stakeholders regarding the cybersecurity incident.
In its regulatory filing, the company stated, "Upon discovering the unauthorized access, we immediately took steps to secure our systems and launched an investigation, with the assistance of leading third-party cybersecurity experts, to determine the nature and scope of the incident." This proactive approach signals a commitment to understanding the breach and mitigating its effects.
A spokesperson for Quest Diagnostics directed inquiries to an FAQ page on the company’s website, which was updated on October 23rd. This page serves as a central hub for information, aiming to provide clarity on the incident, the company’s response, and guidance for individuals who may be affected. The FAQ page, while providing initial information, also underscores the ongoing nature of the investigation, acknowledging that more details may emerge as the forensic analysis progresses.
Quest Diagnostics emphasized that its "core business operations are not impacted and remain up and running." This assurance is critical for maintaining confidence in the company’s ability to continue providing essential laboratory services during this challenging period.
Implications: A Persistent Threat to Healthcare Data
The cybersecurity breach at Quest Diagnostics is not an isolated incident but rather a stark reminder of the escalating threat landscape facing the healthcare industry. This event adds to a growing tally of cyberattacks targeting medical entities, highlighting systemic vulnerabilities that require constant vigilance and robust defense strategies.
A Pattern of Attacks: As noted by The Associated Press, this is not the first time Quest Diagnostics has experienced a data breach. Previous incidents include:
- 2016: A breach exposed lab results and contact information for approximately 34,000 individuals.
- 2019: A significant incident involving a third-party billing provider led to the compromise of personal information for nearly 11.9 million Quest patients.
These past events underscore the persistent nature of cybersecurity risks for large healthcare organizations and the critical need for continuous improvement in data protection measures.
Broader Healthcare Sector Vulnerabilities: Fierce Biotech has pointed out that Quest Diagnostics’ latest breach is symptomatic of a wider trend of cyberattacks impacting the healthcare sector. Other prominent medical device makers, including Abbott, Stryker, Medtronic, and Boston Scientific, have also been targets of cyber intrusions. This indicates a concerted effort by malicious actors to exploit weaknesses within the interconnected digital infrastructure of healthcare.
Beyond Healthcare: The threat extends beyond the healthcare domain, with sectors such as retail grocery, education technology, and utilities also increasingly falling victim to sophisticated cyber threats. This broad spectrum of targeted industries underscores the pervasive nature of cybercrime and the need for robust security measures across all critical infrastructure.
Unrelated to Global Vulnerability: Quest Diagnostics has confirmed that this specific breach is not linked to a separate, widely publicized PHP software vulnerability disclosed earlier in the week. This vulnerability had prompted a global rush for security updates across numerous companies, demonstrating that the Quest Diagnostics incident was an independent intrusion rather than a consequence of a widespread, known software flaw.
The implications of such breaches are profound. Beyond the immediate concern of compromised patient data, these incidents can erode public trust in healthcare institutions, disrupt critical medical services, and lead to significant financial and reputational damage for the affected organizations. The continuous evolution of cyber threats necessitates an equally dynamic and adaptive approach to cybersecurity, involving not only technological safeguards but also comprehensive employee training, rigorous vendor risk management, and proactive threat intelligence. As the investigation into the Quest Diagnostics breach unfolds, the healthcare industry will undoubtedly be scrutinizing its own defenses and seeking to learn from this latest significant event.
